Every embedded system runs on a quiet bargain. The driver believes the sensor. The
application believes the driver. The firmware believes the bus, the bootloader, and whatever
configuration it was handed at startup. Nobody signed that bargain and nobody audits it, but
everything the system does depends on it holding.
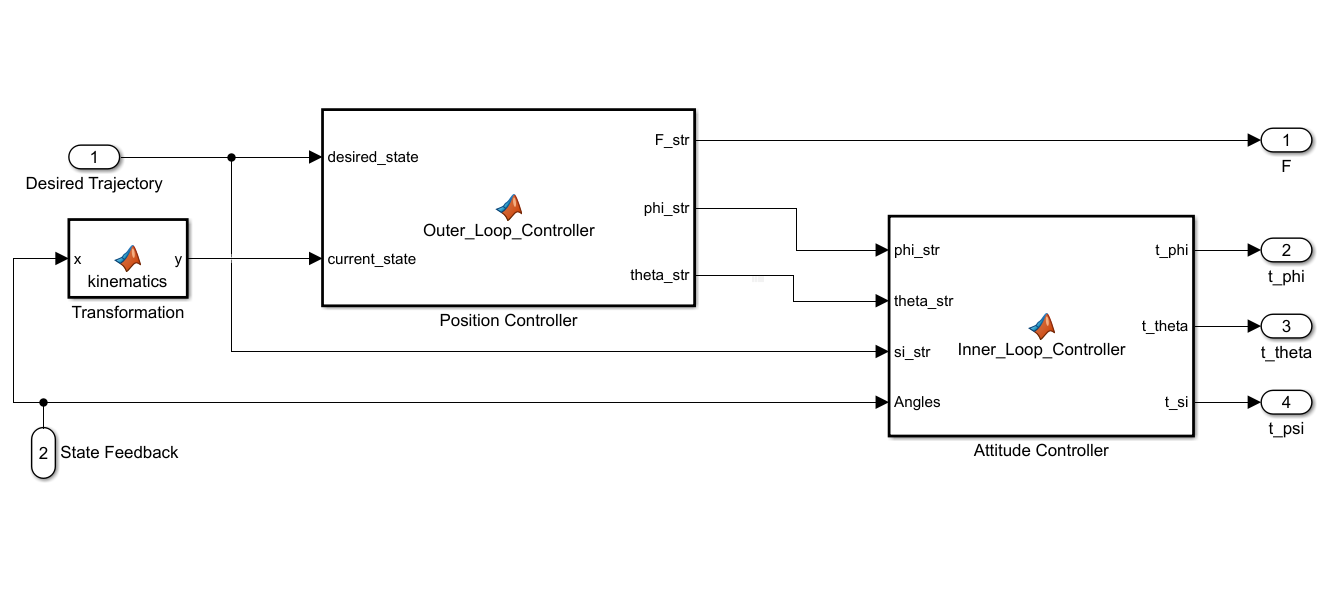
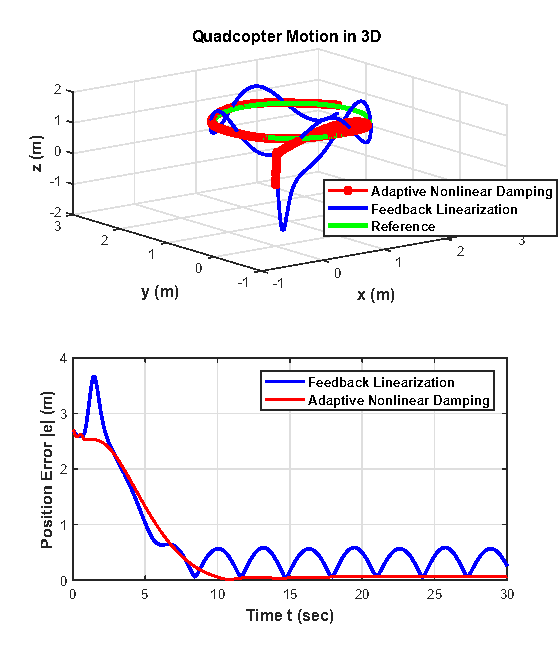
I spent six years on the building side. Real-time control and embedded software in C and C++,
integrated onto hardware where the output moved something physical, from flight controllers to
production automotive software. I learned where the assumptions live,
because whenever a system failed on me, that is where the failure was hiding. Not in the code
that computed. In the code that believed.
Now I study what happens when someone breaks the bargain on purpose. Every
embedded system trusts more than it verifies. My research asks what an attacker can do with
the difference.
I am a PhD student in Computer Science and Engineering at Penn State, in PSecLab within the Institute for Networking and
Security Research, advised by Arslan Khan.